
Overview
Authentication is the process of verifying a user’s identity before granting access to your application. Selecting the right authentication method(s) depends on your organization’s security requirements, user experience preferences, and existing infrastructure.Security
Choose authentication methods that align with your security policies and
compliance requirements.
User Experience
Balance security with a smooth login experience to enhance user adoption.
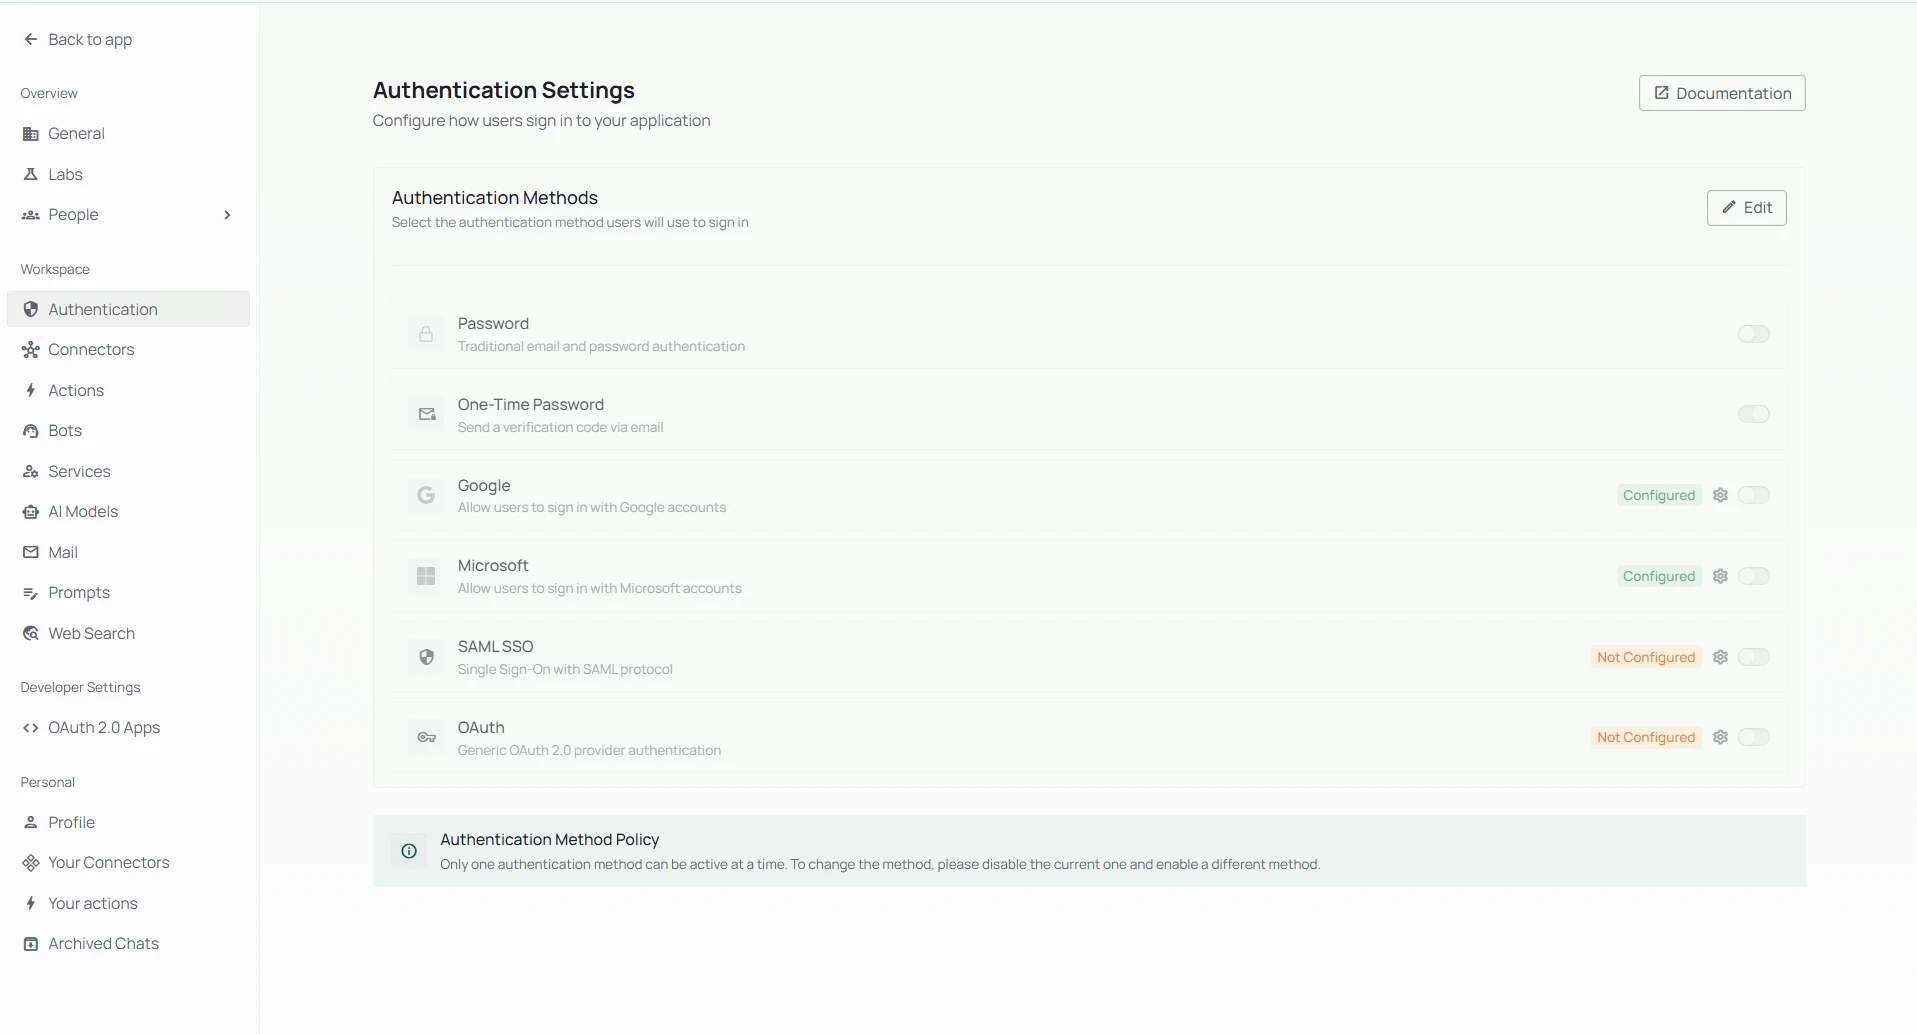
Available Authentication Methods
- Password
- One-Time Password
- Google
- Microsoft/AzureAd
- SAML SSO
Password Authentication
Traditional username and password authentication for your application.For more info, refer to Password Configuration Guide.
Password authentication is the simplest to set up your app.
How sign-in protects accounts
These rules apply whichever methods you turn on.- Only the methods you allow. Sign-in accepts only a method your organization has turned on. In a sign-in with more than one step (for example, a password and then a code sent by email), each step accepts only the methods listed for that step, so the second step can’t be skipped by entering the password again.
- The same person at every step. Every step must be completed by the same account. A step completed with a different account (for example, a colleague’s Google sign-in) is refused with “This step was completed with a different account than the step before it. Start again from the sign-in page and use the same account for every step.”
- No hint about who has an account. Sign-in answers the same way whether or not an email belongs to an account, so nobody can use the sign-in page to find out which addresses are real. A wrong password and an unknown email both get “The email or password is incorrect. Check both and try again, or use Forgot password to set a new password.”
- Locking after repeated failures. After five wrong passwords or codes in a row, the account is locked for 24 hours and then unlocks by itself. The account owner is emailed when the lock is applied. While the lock lasts, sign-in shows the ordinary “incorrect” message, even for the right password or code, because a different message would tell a stranger that the account exists. The lock email is the only place the owner learns about it.
Sign-in steps are set up through the API (
POST /api/v1/orgAuthConfig/updateAuthMethod); the settings page saves a single step. SAML SSO can’t be one of several steps yet: a policy with more than one step that includes SAML is refused. Use SAML on its own, as a one-step sign-in. See SAML SSO.Troubleshooting
If users encounter authentication issues:- Verify the authentication method configuration
- Check server logs for specific error messages
- Confirm network connectivity to identity providers
- Validate certificate expiration dates
- Test authentication flow with a test account
- If someone is sure their password is right but is told it is incorrect, their account may be locked after five failed attempts. Ask them to look for the lock email; the account unlocks 24 hours after the lock was applied